MCP Server Authorization
Model Context Protocol (MCP) is the protocol AI applications (Claude, ChatGPT, Cursor and similar hosts) use to discover and call external tools. MCP servers expose tools; MCP clients invoke them. When an MCP server exposes sensitive resources, it needs authorization to ensure only permitted clients and users can access it.
LumoAuth's role is to authorize those tool calls: register MCP servers as protected resources, configure scopes, and let LumoAuth serve as the OAuth 2.0 authorization server while AI applications act as OAuth clients.
This implementation follows the MCP Authorization specification, revision 2025-11-25, including OAuth 2.1, protected resource metadata (the discovery document an MCP server publishes so clients can find its authorization server), resource indicators (the resource parameter that pins a token to one server), the authorization-server discovery document, the issuer identifier in the authorization response (iss), and Client ID Metadata Documents (a client identifies itself with a URL to a metadata file instead of registering first) — the spec's preferred client registration mechanism. It also covers the accepted spec enhancements: SEP-835 (default scopes advertised in the 401 challenge), SEP-837 (application_type validation in dynamic client registration), SEP-2350 (incremental scope consent on step-up), SEP-2351 (standardized well-known URI suffix), and SEP-2352 (registration-credential-to-issuer binding).
Architecture
Key concepts
Roles
| Role | Description | In LumoAuth |
|---|---|---|
| Authorization Server | Issues access tokens and handles user authentication | LumoAuth serves this role |
| Resource Server (MCP Server) | Hosts tools, resources, and prompts; validates Bearer tokens | Your registered MCP server |
| Client (MCP Client) | AI application that connects to MCP servers on behalf of users | Registered as an OAuth client in LumoAuth |
Standards implemented
| Standard | Purpose |
|---|---|
| OAuth 2.1 | Core authorization framework with security best practices |
| Protected resource metadata | How MCP clients discover the authorization server for an MCP server |
| Resource indicators | Binding tokens to a specific MCP server audience |
| Discovery document | Discovering LumoAuth's endpoints |
| Dynamic client registration | MCP clients can register themselves through the API |
| Issuer identifier in the response | The iss parameter on the redirect back, which prevents mix-up attacks |
| Client ID metadata documents | URL-based client identity, preferred by MCP 2025-11-25 |
The exact specifications are listed in Standards used on this page.
Quickstart
To secure an MCP server with LumoAuth:
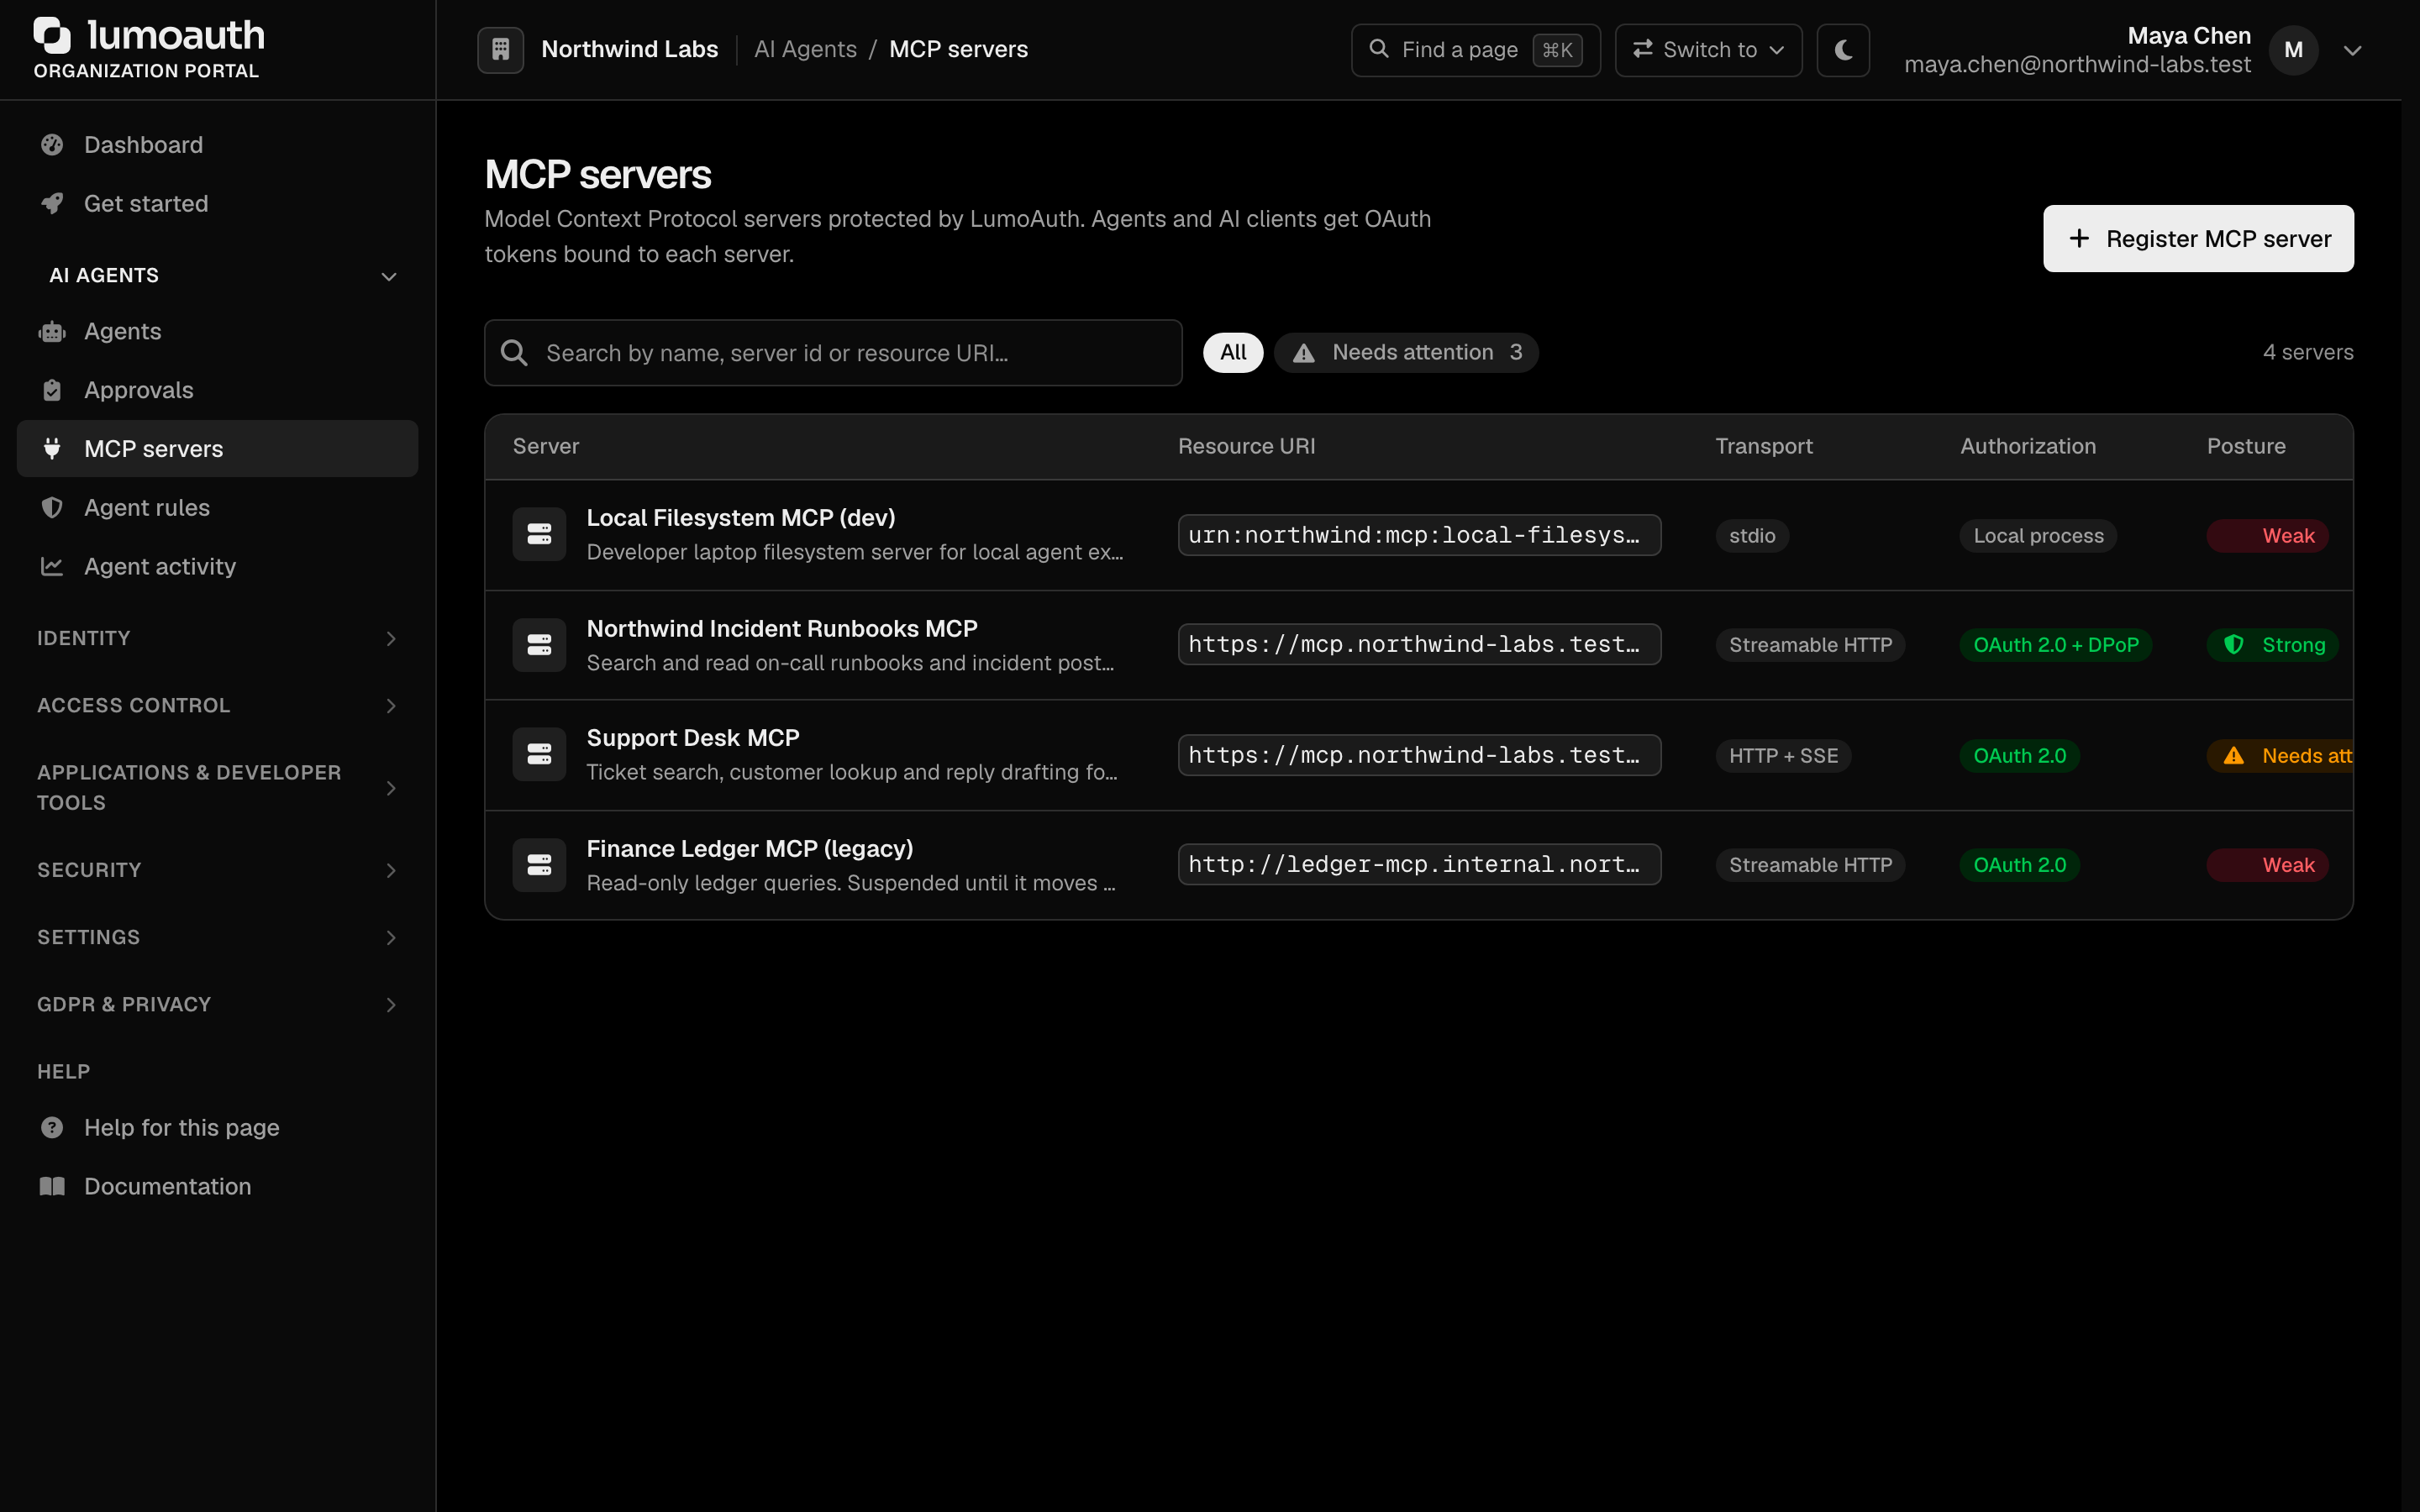
- Register your MCP server in the Organization Portal under AI Agents → MCP servers (click Register MCP server).
- Configure your MCP server to return
401 Unauthorizedwith aWWW-Authenticateheader pointing to LumoAuth's Protected Resource Metadata. - Validate tokens using LumoAuth's token introspection endpoint, verifying that the
audclaim matches your server's Resource URI.
API endpoints
GET /orgs/{orgId}/api/v1/.well-known/oauth-protected-resource/mcp/{serverId} — protected resource metadata for a specific MCP server. View details →
GET /orgs/{orgId}/api/v1/.well-known/oauth-protected-resource — root-level Protected Resource Metadata for the organization's MCP servers. View details →
GET /orgs/{orgId}/api/v1/mcp/servers — list all active MCP servers for an organization. The caller needs the settings.manage permission; an API key additionally needs the mcp:read scope. View details →
GET /orgs/{orgId}/api/v1/mcp/servers/{serverId} — details of a specific MCP server including discovery URLs. View details →
GET / POST /orgs/{orgId}/api/v1/mcp/{serverId}/challenge — test the 401 challenge flow. Returns the WWW-Authenticate header for unauthenticated requests. View details →
Related
- MCP Authorization Flow — step-by-step OAuth 2.1 flow
- Protected Resource Metadata — discovery document details
- MCP Server Registration — register your MCP server
- Client ID Metadata Documents — URL-based client registration
Standards used on this page
| Plain name | Standard |
|---|---|
| Protected resource metadata | RFC 9728 |
| Resource indicators | RFC 8707 |
| Discovery document | RFC 8414 |
| Issuer identifier in the response | RFC 9207 |
| Client ID metadata documents | OAuth Client ID Metadata Document (draft) |
| Dynamic client registration | RFC 7591 |
| Model Context Protocol (MCP) authorization | MCP Authorization specification |
See the standards reference for what each one covers and how LumoAuth uses it.